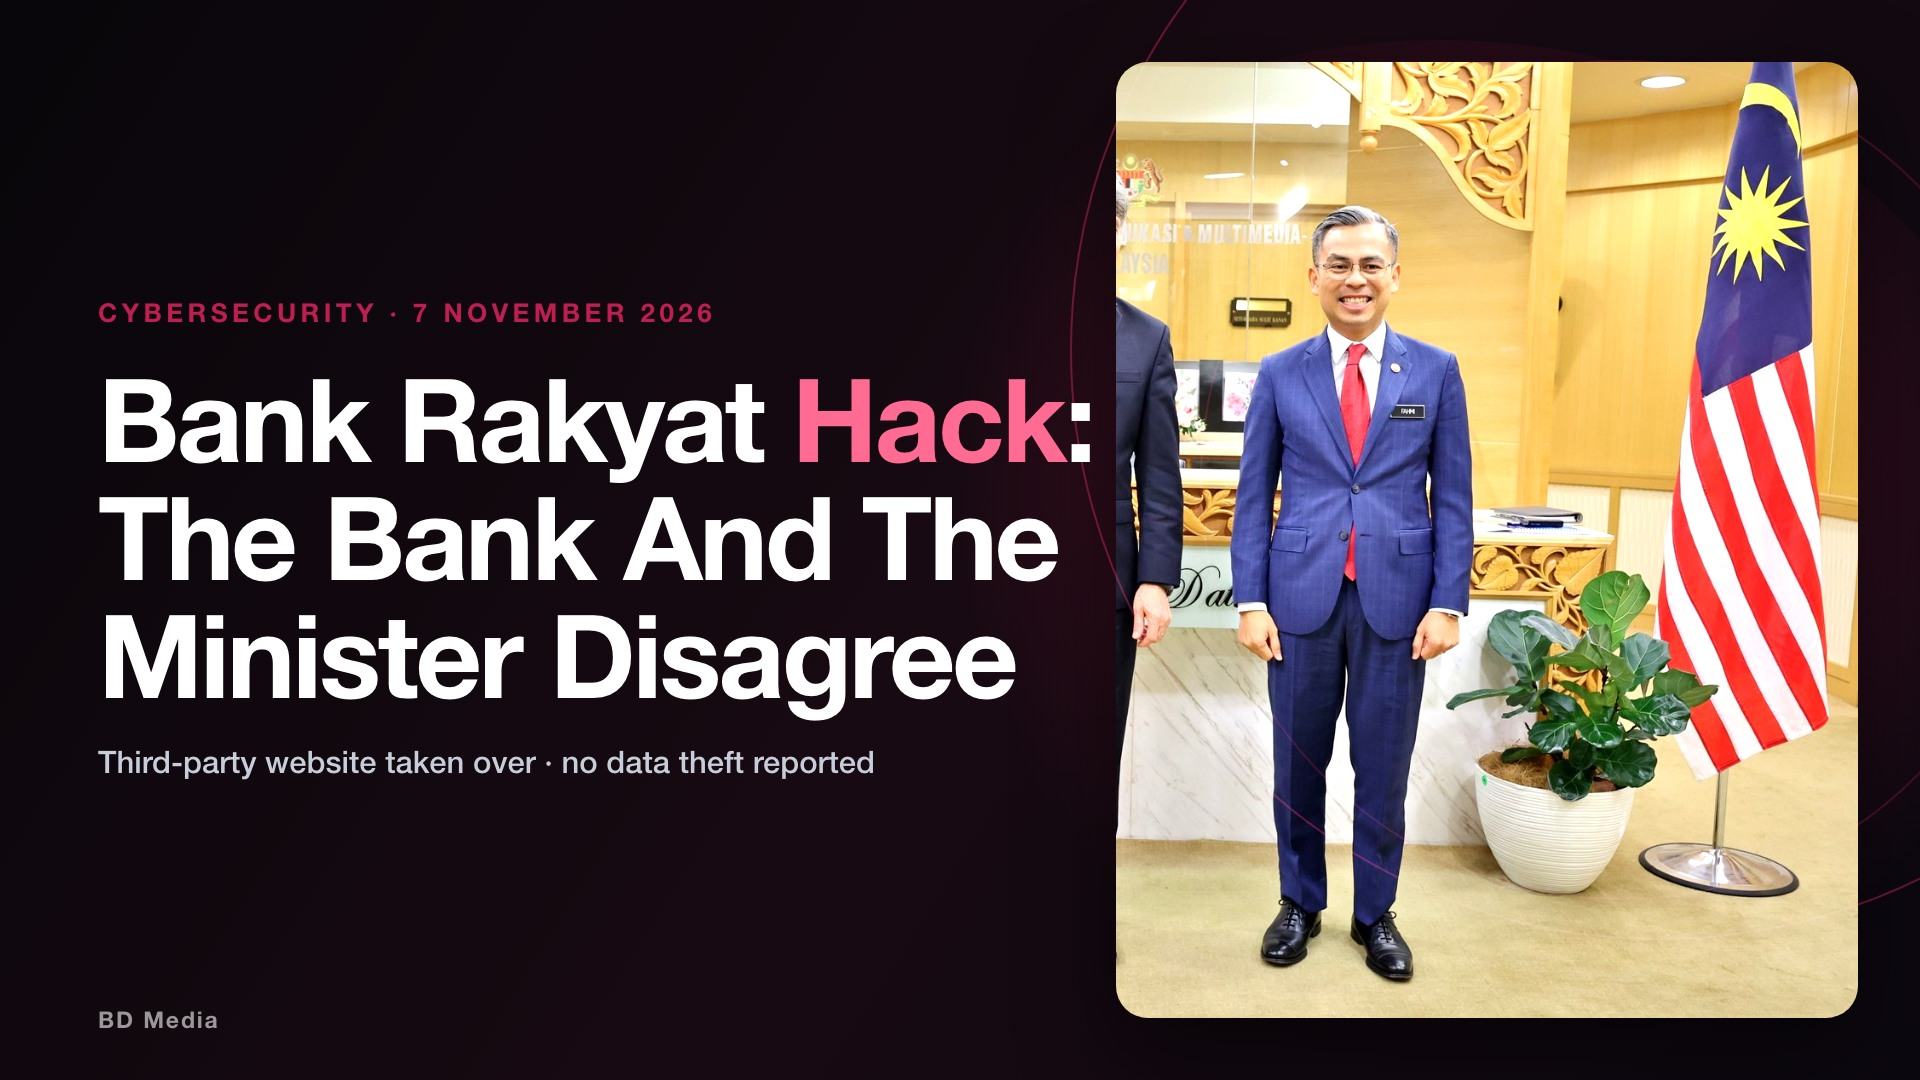
The Bank Rakyat hack became a matter of public record on Saturday, 7 November, when Communications Minister Datuk Seri Fahmi Fadzil told reporters in Doha that the bank had reported its third-party-managed website hacked, with the damage confined to web defacement. The bank itself, in a statement on Facebook the same day, attributed the disruption of its corporate website to “a technical issue with a third-party service provider’s system” and said customer data and deposits were safe. A defacement and a technical fault are not the same thing, and the gap between the two statements is the part of this story a Malaysian SME should actually read.
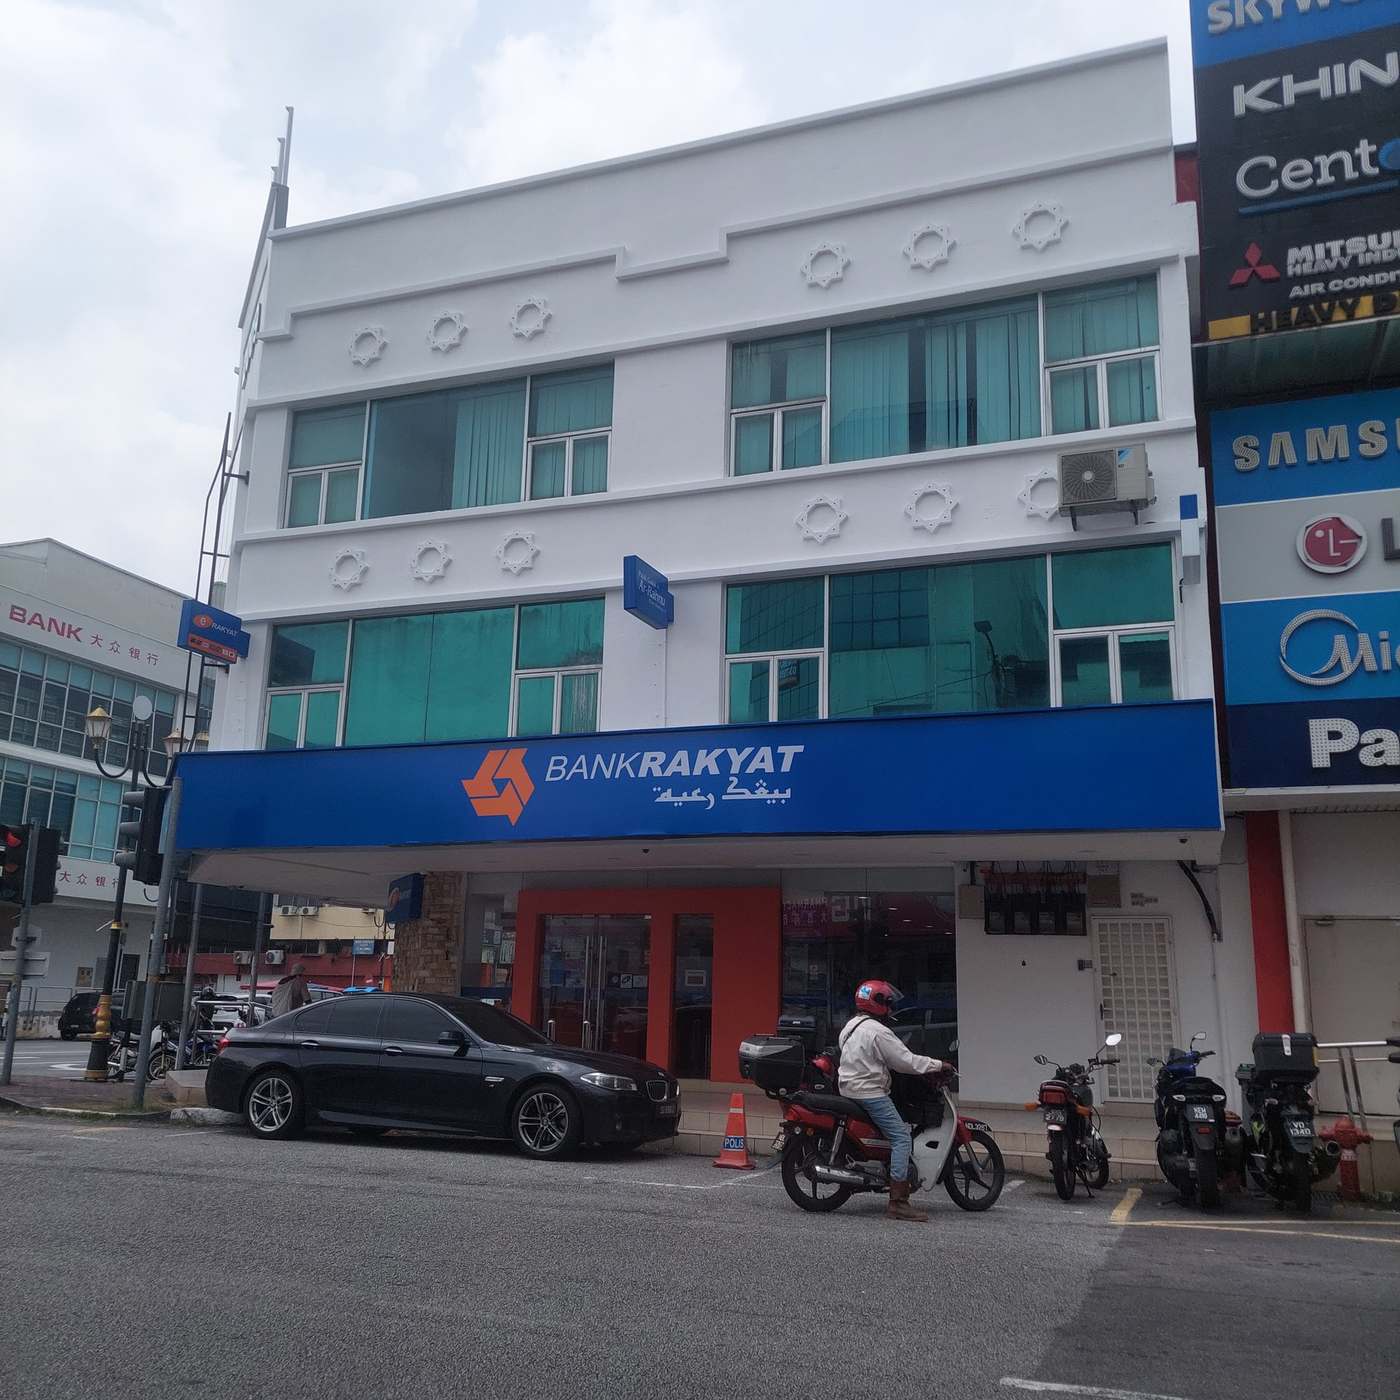
A Bank Rakyat branch in Seremban. The bank’s systems and customer deposits were reported unaffected; the damage was to its public website. Photo: Ardzun / Wikimedia Commons, CC BY-SA 4.0, taken 2 July 2025.
What the Bank Rakyat hack actually took out
The sequence, from the public statements:
| When | What was said, and by whom |
|---|---|
| Fri 6 Nov, about 11.30pm | Bank Rakyat tells customers its corporate website is temporarily inaccessible, points them at alternative channels, and names no cause |
| Late Fri 6 Nov | Lowyat.NET reports that banking pages, including the iRakyat online banking login page, had been defaced, and that a threat actor using the name MARLANWG claimed the act |
| Sat 7 Nov | The bank’s Facebook statement: the disruption is confined to the corporate website, caused by a technical issue with a third-party service provider; banking systems, deposits and customer data unaffected |
| Sat 7 Nov, Doha | Fahmi Fadzil, asked about attacks on Malaysian targets: no data theft and no disruption to online banking; the Bank Rakyat website was hacked and taken over, and users were redirected to i-Rakyat, a site the bank fully owns |
| Fri 6 Nov, Cabinet | The Prime Minister calls for a broader cybersecurity review across government assets, banks and government-linked companies, following an earlier order to the National Security Council |
Source: the bank’s statement as published by The Edge Malaysia and NST on 7 November 2026; Fahmi Fadzil’s remarks as published by Bernama on 7 November 2026; Lowyat.NET, 7 November 2026.
Three things are agreed by everyone: the website was unavailable, customers could still bank through iRakyat and the bank’s app, and no theft of customer data has been reported. What is not agreed is what happened to the server. A defacement is not a technical fault. It means someone with write access to the site replaced what visitors saw. The bank has not confirmed a hack; the minister says the bank reported one. Both statements stand unqualified on the record as of 7 November.
What is not yet known: whether any customer data was read, who MARLANWG is, how access was gained, and whether the third-party provider has published anything at all. No incident report has been released. This page will be updated when one is.
Two officials, two descriptions of the same server
Fahmi Fadzil is the MADANI Government spokesperson as well as Communications Minister, and he was answering a Malaysian in Qatar when he set out the position. Two passages from his remarks, as published by Bernama, carry it in his own words.
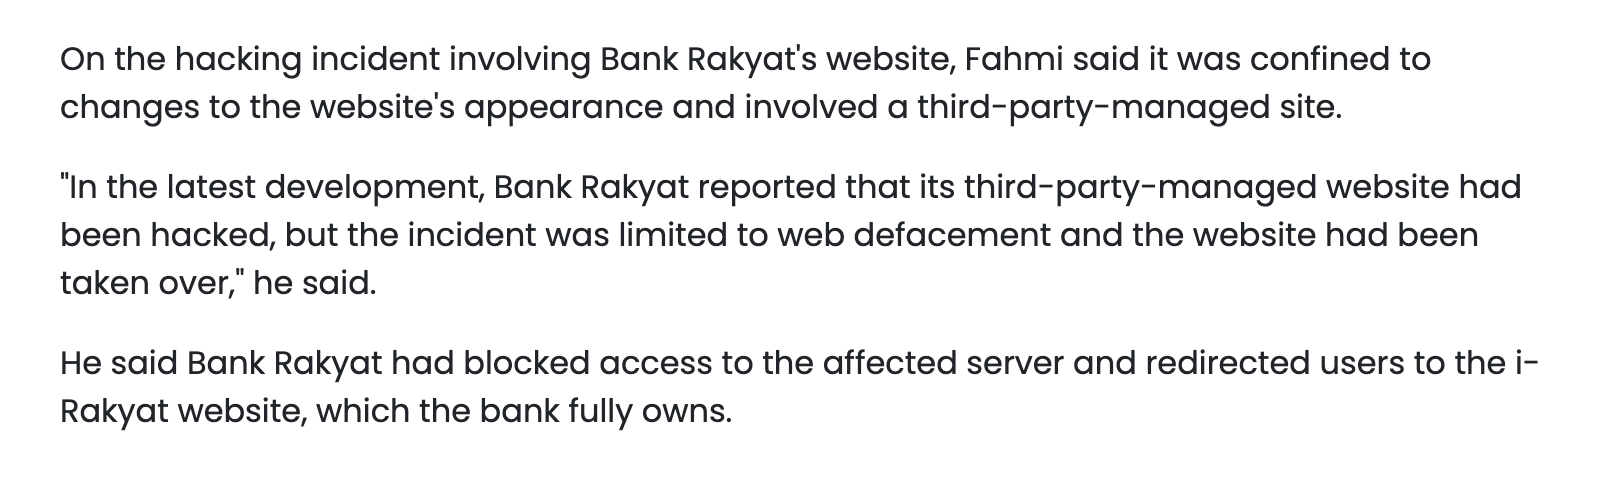
Source: Bernama, 7 November 2026. Captured 7 November 2026 from https://www.bernama.com/en/news.php?id=2631400
The bank’s own words, carried by The Edge Malaysia and NST the same day, do not use the word hack. “We wish to assure customers that Bank Rakyat’s banking systems and operations continue to function as usual, while customers’ personal data, banking information and savings remain safe and unaffected,” the statement said, before naming a third-party technical issue as the cause.
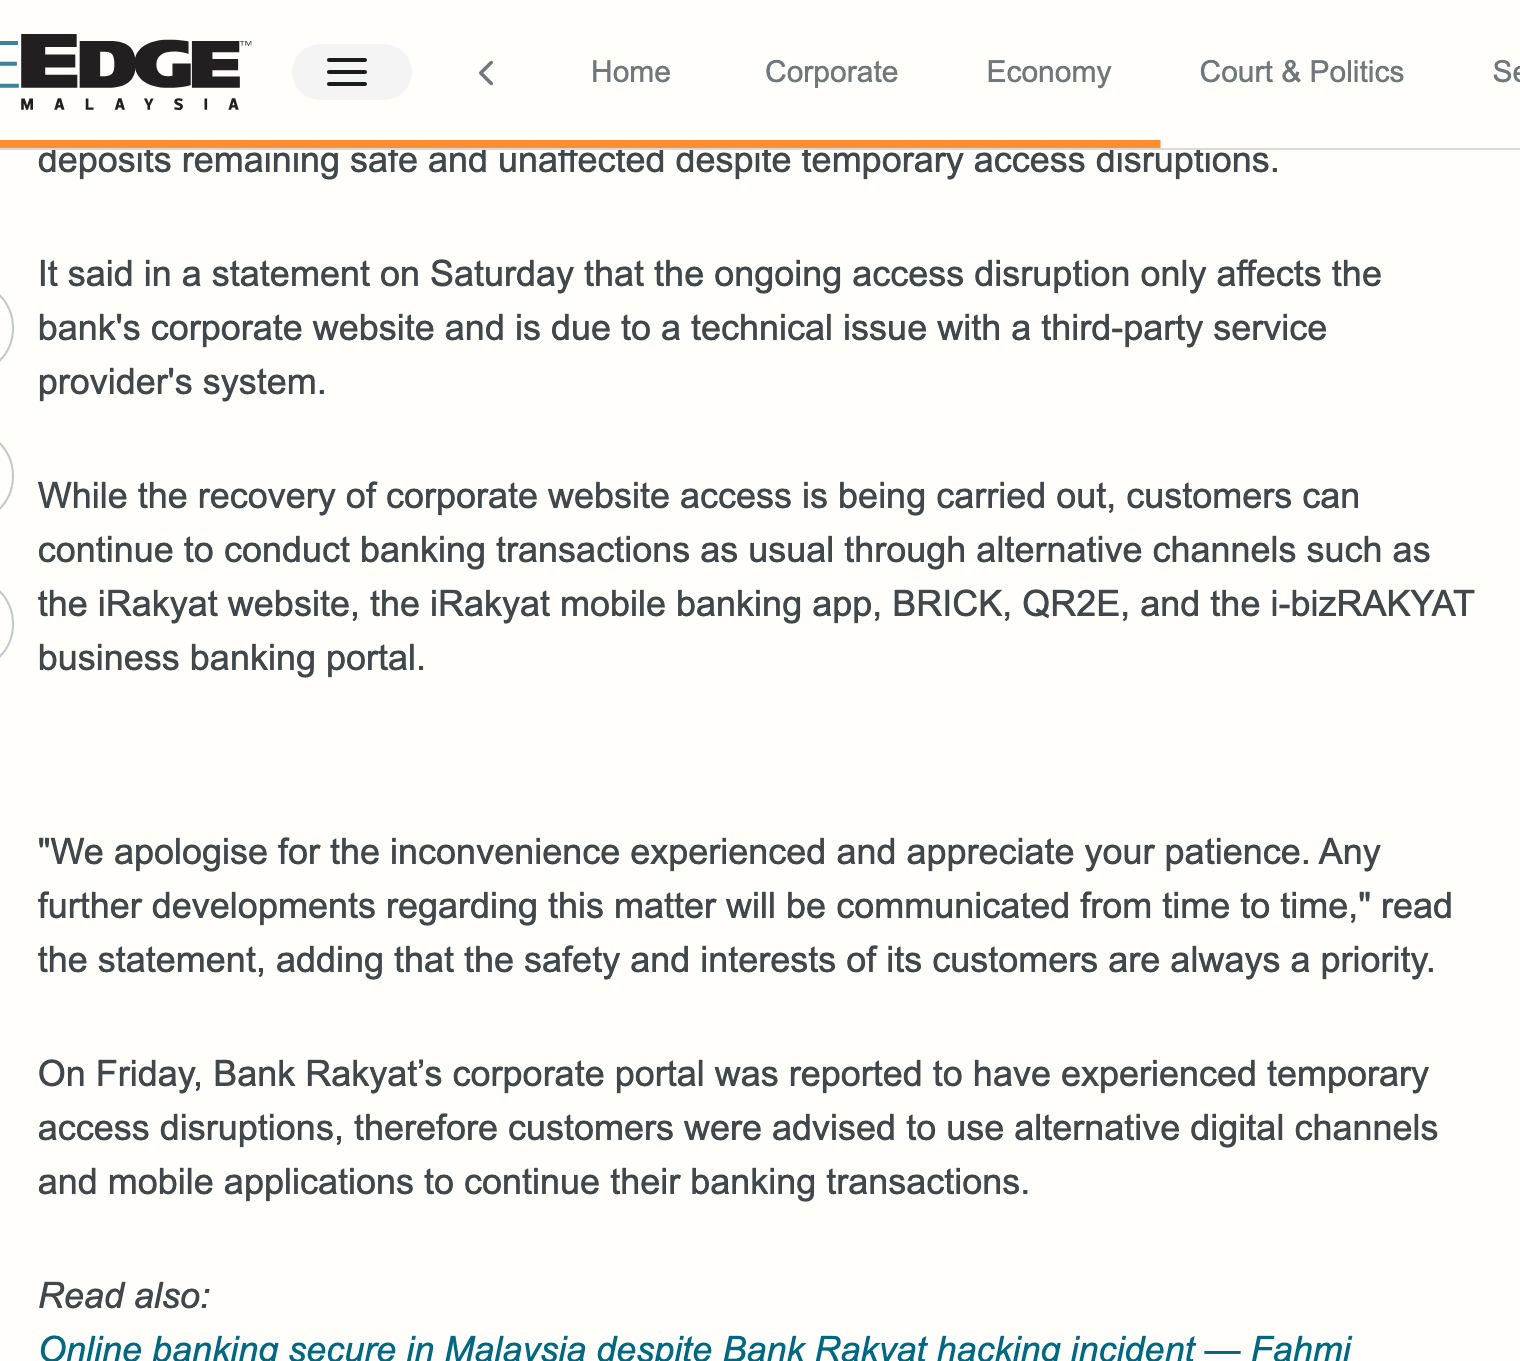
Source: The Edge Malaysia, 7 November 2026, which quotes the bank’s statement in full. Captured 7 November 2026 from https://theedgemalaysia.com/node/824961
Lowyat.NET’s reporting is the third account, and the most uncomfortable one: it places the defacement on banking pages, including the iRakyat login page, not on a marketing site. The bank has not confirmed that. If Lowyat is right, the phrase “corporate website only” in the bank’s statement is wrong. Nobody with authority has settled it, so the safe reading for a customer is that the scope of the intrusion is contested.
The regulator has already priced a failure like this
The January precedent is the reason this is not just a bank’s bad weekend. On 20 January 2026, Bank Negara Malaysia imposed a RM1 million administrative monetary penalty on Bank Rakyat for breaches of its technology risk management and customer information protection requirements, following a cybersecurity incident in which an external threat actor gained unauthorised access to the bank’s IT infrastructure. The bank paid on 26 January 2026.
Bernama quoted the central bank’s reasoning in a way that should be read by anyone who outsources their website and assumes the outsourcing transfers the risk:
Nothing in that penalty concerned the third party. It concerned the entity that held the customer information. The regulator fined the bank, not the vendor, because in the regulator’s frame the entity owns the outcome of whatever its supplier does. That is the standing rule this incident lands on.
What a third-party-managed website actually means
Most Malaysian SMEs are in the same architecture as the bank. The company owns the domain and the customer relationships; an agency or a freelancer holds the administrative access to the website, the hosting account, or both. When that supplier’s access is compromised, the defacement is the visible part and usually the least expensive part. The same access that rewrites a homepage can plant a page that harvests card details, redirect payment traffic, or sit quietly reading enquiry forms that arrive by email.
The bank’s incident also shows the difference between a defacement and a data breach in the eyes of the customer. The bank spent Saturday reassuring customers that deposits and data were safe, which is itself evidence of what customers were asking. A website that is quietly compromised reads no differently to its owner until someone else points at it.
Four questions to put to whoever runs your website
None of this requires a security team, and the first two take an email. Ask them this week, in writing, so the answers exist before they are needed.
- Who holds administrative access, and to what? Get the list: domain registrar, hosting control panel, CMS administrator, DNS, and the email account that can reset all of them. If one person holds all five and that person is unreachable, that is the finding.
- Has anyone enabled multi-factor authentication on those accounts? A defaced WordPress site usually got that way through a reused or phished password. The control that stops the most attacks costs nothing.
- If the site is defaced tonight, who does what, and by when? You want a named person, a restoration source, and a number of hours, not a promise. The bank’s own playbook, visible on Saturday, was to take the server offline and redirect customers to a channel it fully owned. Yours should have an equivalent.
- What would you have to tell customers, and when? If your site collects enquiries, payments or personal data, a compromise is also a personal data question. Decide before an incident who makes that call, because a Saturday morning is the wrong time to read a policy document for the first time.
What to watch next
Three things will settle the questions this incident leaves open. Whether Bank Rakyat publishes its own account, which would resolve the conflict between “technical issue” and “hacked”. Whether the actor Lowyat named is linked to other Malaysian targets, which would show whether this was opportunistic or directed. And what comes out of the Cabinet-ordered review, since a review of government assets, banks and GLCs usually produces the requirements that later flow down to their suppliers, which is where SMEs meet them.
Read next: Zero Trust Malaysia: what MACC’s 90,000 daily attacks should change for an SME covers the controls, and WhatsApp Scam Malaysia: RM327,000 lost in two transfers covers the human route into the same accounts.
Last updated: 7 November 2026. The bank has not confirmed a cyberattack; the minister’s account and the bank’s account are both on the record and differ. No incident report has been published at the time of writing.
Sources
- Bernama, Online Banking System Remains Secure – Fahmi, 7 November 2026 (Fahmi Fadzil’s account of the hack, the defacement, the redirection to i-Rakyat, and the Cabinet-ordered review) — bernama.com
- The Edge Malaysia, Access disruptions: Bank Rakyat assures customer information and savings safe, 7 November 2026 (the bank’s statement, the third-party technical issue, the alternative channels) — theedgemalaysia.com
- NST, Bank Rakyat assures customers data safe amid website disruption, 7 November 2026 (independent confirmation of the bank’s statement) — nst.com.my
- Lowyat.NET, Bank Rakyat Takes Down Sites After Suspected Cyber Attack, 7 November 2026 (the reported defacement of the iRakyat login page; the threat-actor claim; unconfirmed by the bank) — lowyat.net
- The Star, QuickCheck: Are a local bank’s customers at risk after its online services went down?, 7 November 2026 (the verdict, the bank’s assurance, and the RM1 million Bank Negara penalty reported earlier this year) — thestar.com.my
- Bernama, BNM Fines Bank Rakyat RM1 Mln For Cybersecurity, Customer Information Protection Breaches, 1 April 2026 (the RM1 million administrative monetary penalty, imposed 20 January 2026 and paid 26 January 2026) — bernama.com
- Wikimedia Commons, Bank Rakyat in Seremban, CC BY-SA 4.0 (cover photograph) — commons.wikimedia.org
- Own captures, 7 November 2026: the Bernama report and The Star QuickCheck page, cropped to the quoted passages. Read-only.
BD Media is the editorial desk of Big Domain. This article reports statements made on 6 and 7 November 2026 by Bank Rakyat, by Communications Minister Fahmi Fadzil and by Bank Negara Malaysia, as published by the outlets listed above. It is not security advice for any specific system.